
Firefox on Windows only requests a USB security key for my Meta passkey instead of allowing my iPhone passkey

I use Firefox on Windows to manage Meta Business Suite for my business, Goff Housing Solutions. Facebook, Meta Business Suite and Ads Manager all open normally in Firefox.
The problem occurs when I open the protected Meta Business Portfolio Settings. Meta requires my existing passkey for accounts.meta.com. After I click Continue, Firefox invokes Windows Security, but the only authentication method presented is:
“Security key — Insert your security key into the USB port.”
I have never owned or configured a physical USB security key.
I confirmed that the correct accounts.meta.com passkeys are stored in Apple Passwords on my iPhone. The iPhone can access Meta Business Suite and the protected Business Portfolio Settings normally.
As a control test, I opened the same Meta/Facebook account and the same Goff Housing Solutions Business Portfolio on this same Windows computer using Google Chrome. Chrome opens the protected Business Portfolio Settings successfully.
Therefore, my Meta account, Business Portfolio, permissions, 2FA and existing passkey appear to be working. The problem seems specific to Firefox/Windows passkey handling: Firefox/Windows is treating the authentication request as requiring a physical USB security key rather than offering the existing passkey on my nearby iPhone (for example via QR code/phone authentication).
How can I make Firefox on Windows use my existing accounts.meta.com passkey from my iPhone instead of requesting a physical USB security key?
I do not want to delete/recreate my Meta passkeys, disable 2FA, reset my Meta account, or create a new Business Portfolio because all of those are currently working.
All Replies (8)
Hi,
I'm not sure using a remote security key is part of the default protocol... Maybe Meta does some special handling for Chrome?
In any case, your report is super valuable, since most people (and QA) are not able to access such specific paid products. Could you please file a bug for this issue so that our team could try to investigate? If so, please share a link to it here.
Also, more info about what happens in Chrome would be very helpful. Does it just silently sign you in, or does anything special happen (you need to scan a QR code etc.)?
Chrome has its own custom Passkey store coming from Google's ecosystem Wallet as credential provider across devices, so they bolted on the Chrome implementation irrelevant of the operating system on top of that.
Firefox only ever uses whichever operating system capabilities are exposed to it, so this is all based on how your Windows Hello is capable of cross–device authentication.
Looking at the OS from the support log: Windows_NT 10.0 26200 — that's 25H2 if I'm not mistaken, the scenario you're describing should be available to you since 23H2 (or even 22H2 with some KB updates) — so it is generally expected to work. (Older unpatched W11 and also W10 won't be able to do this FIDO CTAP “hybrid” transport.)
This is the breakdown: https://passkeys.dev/docs/reference/windows/
If you try with some of the demo workflows on the passkey showcase sites as https://webauthn.io/ — do they exhibit the same, so you can't really use the cross–device auth at all in Firefox, or these work and the Meta sign–in flow relies on something else?
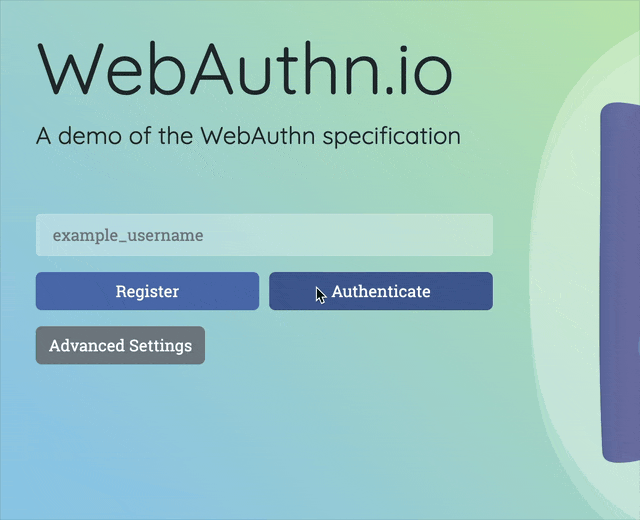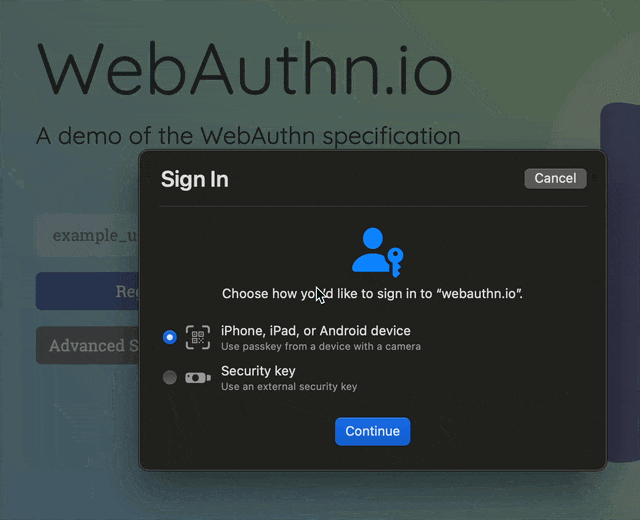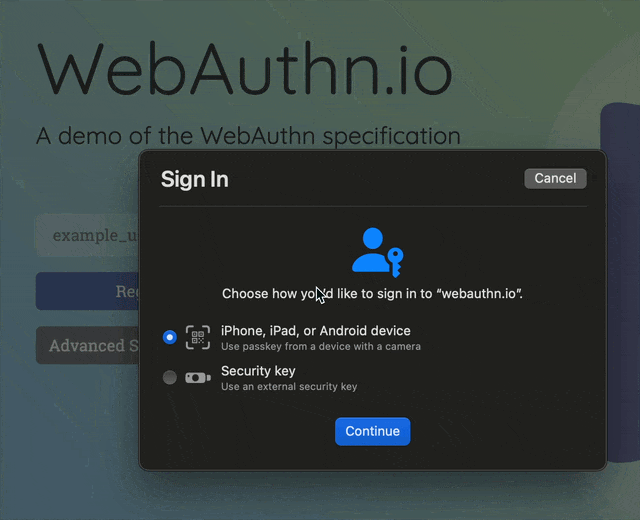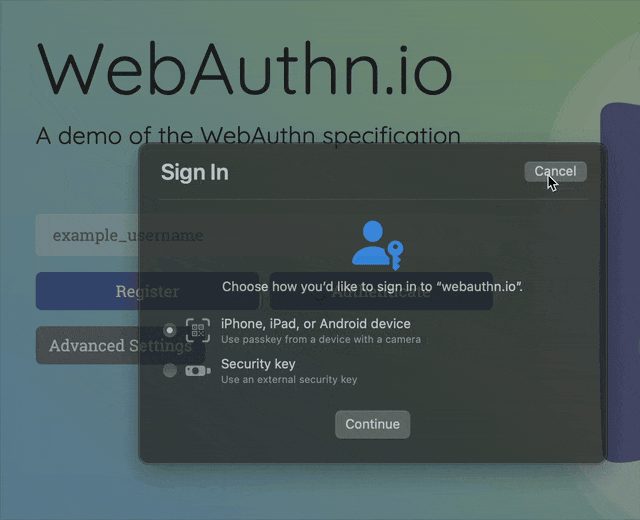
I tested in Firefox at webauthn.io as you suggested. On Register, Windows Security offered only: - This Windows device - Microsoft Password Manager - Security key There was no nearby phone/iPhone/QR/cross-device option. I chose “This Windows device,” entered my Windows Hello PIN, and the registration failed with: “The authenticator was unable to process the specified options, or could not create a new credential.” So this appears reproducible outside Meta as well. My system is Windows 11 25H2, build 26200.9457. Does that point to Windows Hello / WebAuthn hybrid transport not functioning correctly on this machine? What Windows component or setting should I check next?
OK: And if you skip creating anything on that page, and leaving just the defaults in the form and clicking the "Authenticate" button right away… do you get any options from Hello, or the USB stick is the only dialog content?
I tried exactly that: refreshed webauthn.io, left example_username unchanged, did not click Register, and clicked Authenticate directly. No Windows Hello/Security dialog appeared. Webauthn.io immediately returned: “That username has no registered credentials.” So I never reach a Windows dialog where I can see whether phone/QR/cross-device authentication is offered. What would you like me to try next to test the authentication side without first creating a credential?
(Now you got me, I actually don't know if the Hello capability to not just 2FA/passwordless, but also usernameless binding when unavailable exhibits with this kind of an API fail…)
Sorry if this is a dumb question, but does your Windows have Bluetooth enabled, and you're not somehow filtering the capabilities or connections? (or, this is not an enterprise install per se, that might have some system specifics set in certain ways? E.g. the passkey system functionality might need accepting some privacy policy, you might be able to find that in your Windows Settings > Privacy & security > Passkey access.)
Windows should log something in the latter failed case too in Event Viewer: Applications and Services Logs › Microsoft › Windows › WebAuthN › Operational
You can also check WebAuthn has the usual things allowed on the browser side if you open Configuration Editor for Firefox and search for "webauthn":
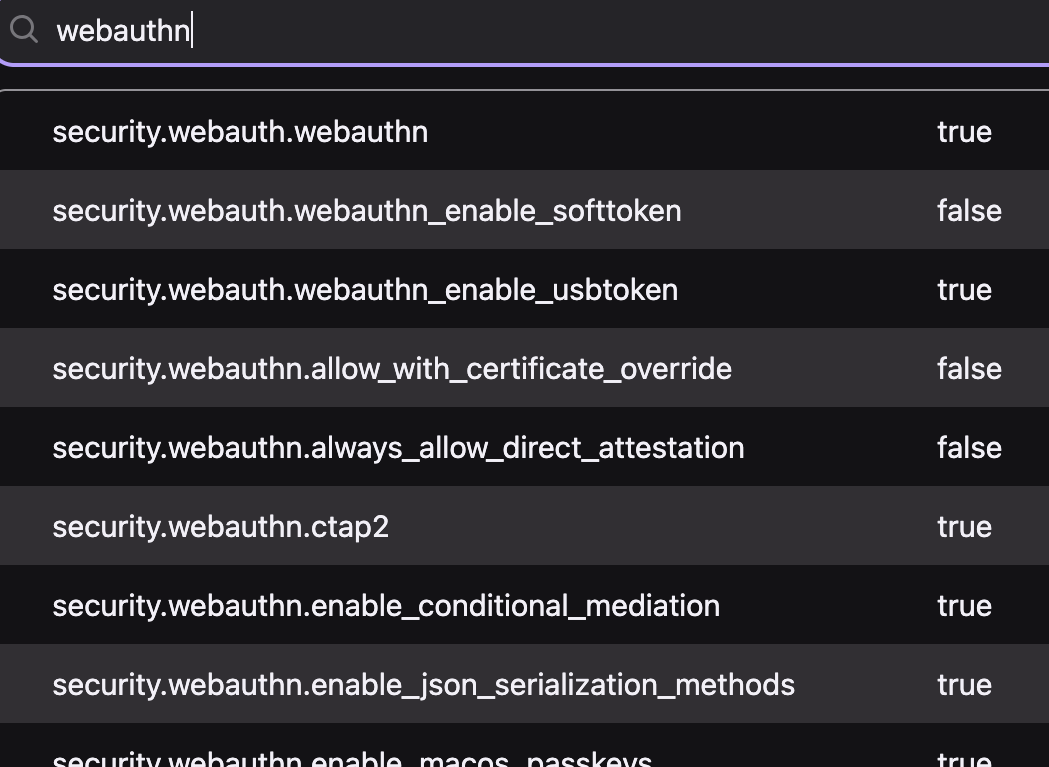
Modified by jbr
I checked Bluetooth as you suggested. Windows Settings has no Bluetooth on/off toggle at all. I then checked Device Manager, and there is no Bluetooth category or Bluetooth adapter listed anywhere. So Windows 11 currently does not detect Bluetooth hardware on this desktop. That seems like it could explain why Windows Hello/WebAuthn never offers the iPhone/cross-device option. Would adding a Windows 11-compatible Bluetooth adapter be sufficient for CTAP hybrid/cross-device passkeys, or are there specific Bluetooth requirements I should look for?
I'm unfortunately not sure as that is a Microsoft question per se — users are generally instructed to verify the built–in integrated BT chip is available — not sure which kind of specs is necessary for the security footprint of this exchange (it's mostly proximity gating as far as I can tell) in case of adding external HW (and driver SW as well regarding compatibility/support…)