Since I uninstalled avast! antivirus and installed Bitdefender Internet Security 2015 Thunderbird asks whether to accept an invalid certificate.

Since I uninstalled avast! antivirus and installed Bitdefender Internet Security 2015 Thunderbird asks whether to accept an invalid certificate when trying to receive new messages.
Please have a look at the two attachments (there seems to be a problem with uploading jpg files).
Obviously Bitdefender manipulates the certificate (probably to be able to scan the mails via SSL connection). But I'm not sure.
Would you recommend to confirm an exception for this certificate (permanently)?
Thanks in advance.
Greetings
Marco
Ɖɔɖɔɖo si wotia
Thank you, christ1.
I found out that after disabling SSL Scanning in Bitdefender, this issue no longer exists.
Maybe this can be considered as confirmation that this certificate really belongs to Bitdefender. Because that's actually what I'm concerned about, i.e. how to validate this certificate to make sure that Bitdefender is the issuer.
All Replies (3)
Added two attachments.
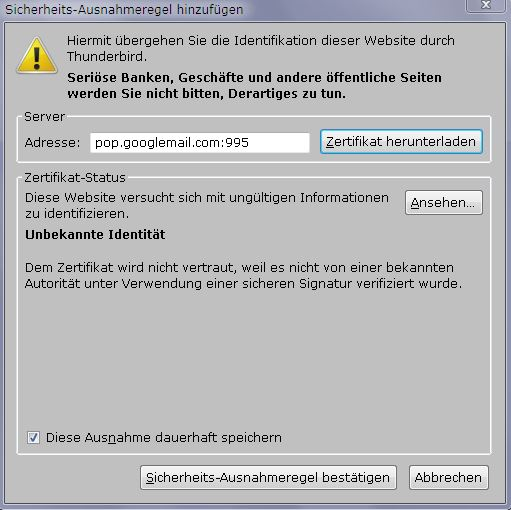
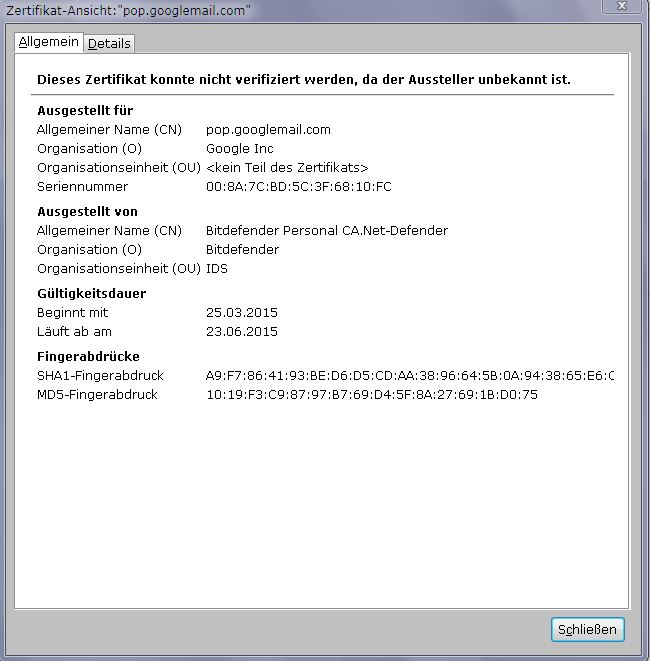

Bitdefender issues a certificate for pop.googlemail.com, i.e. it intercepts your secure connection to the server. One could call this also a 'man in the middle' attack. It's not something I'd be happy with. Whether you trust Bitdefender or not is up to you.
Ɖɔɖɔɖo si wotia
Thank you, christ1.
I found out that after disabling SSL Scanning in Bitdefender, this issue no longer exists.
Maybe this can be considered as confirmation that this certificate really belongs to Bitdefender. Because that's actually what I'm concerned about, i.e. how to validate this certificate to make sure that Bitdefender is the issuer.